
SOVEREIGN ISOLATION & CONTINUOUS GOVERNANCE
Security & Compliance At Core of platform
Xsphere environments are engineered from the physical drive up for organizations that cannot compromise on data sovereignty—combining 100% dedicated, never-reused storage and single-tenant bare metal with real-time Key Security Indicators (KSIs) and architecture built to meet rigorous federal and commercial standards.
THREAT MONITORING
See Every Threat, In Real Time
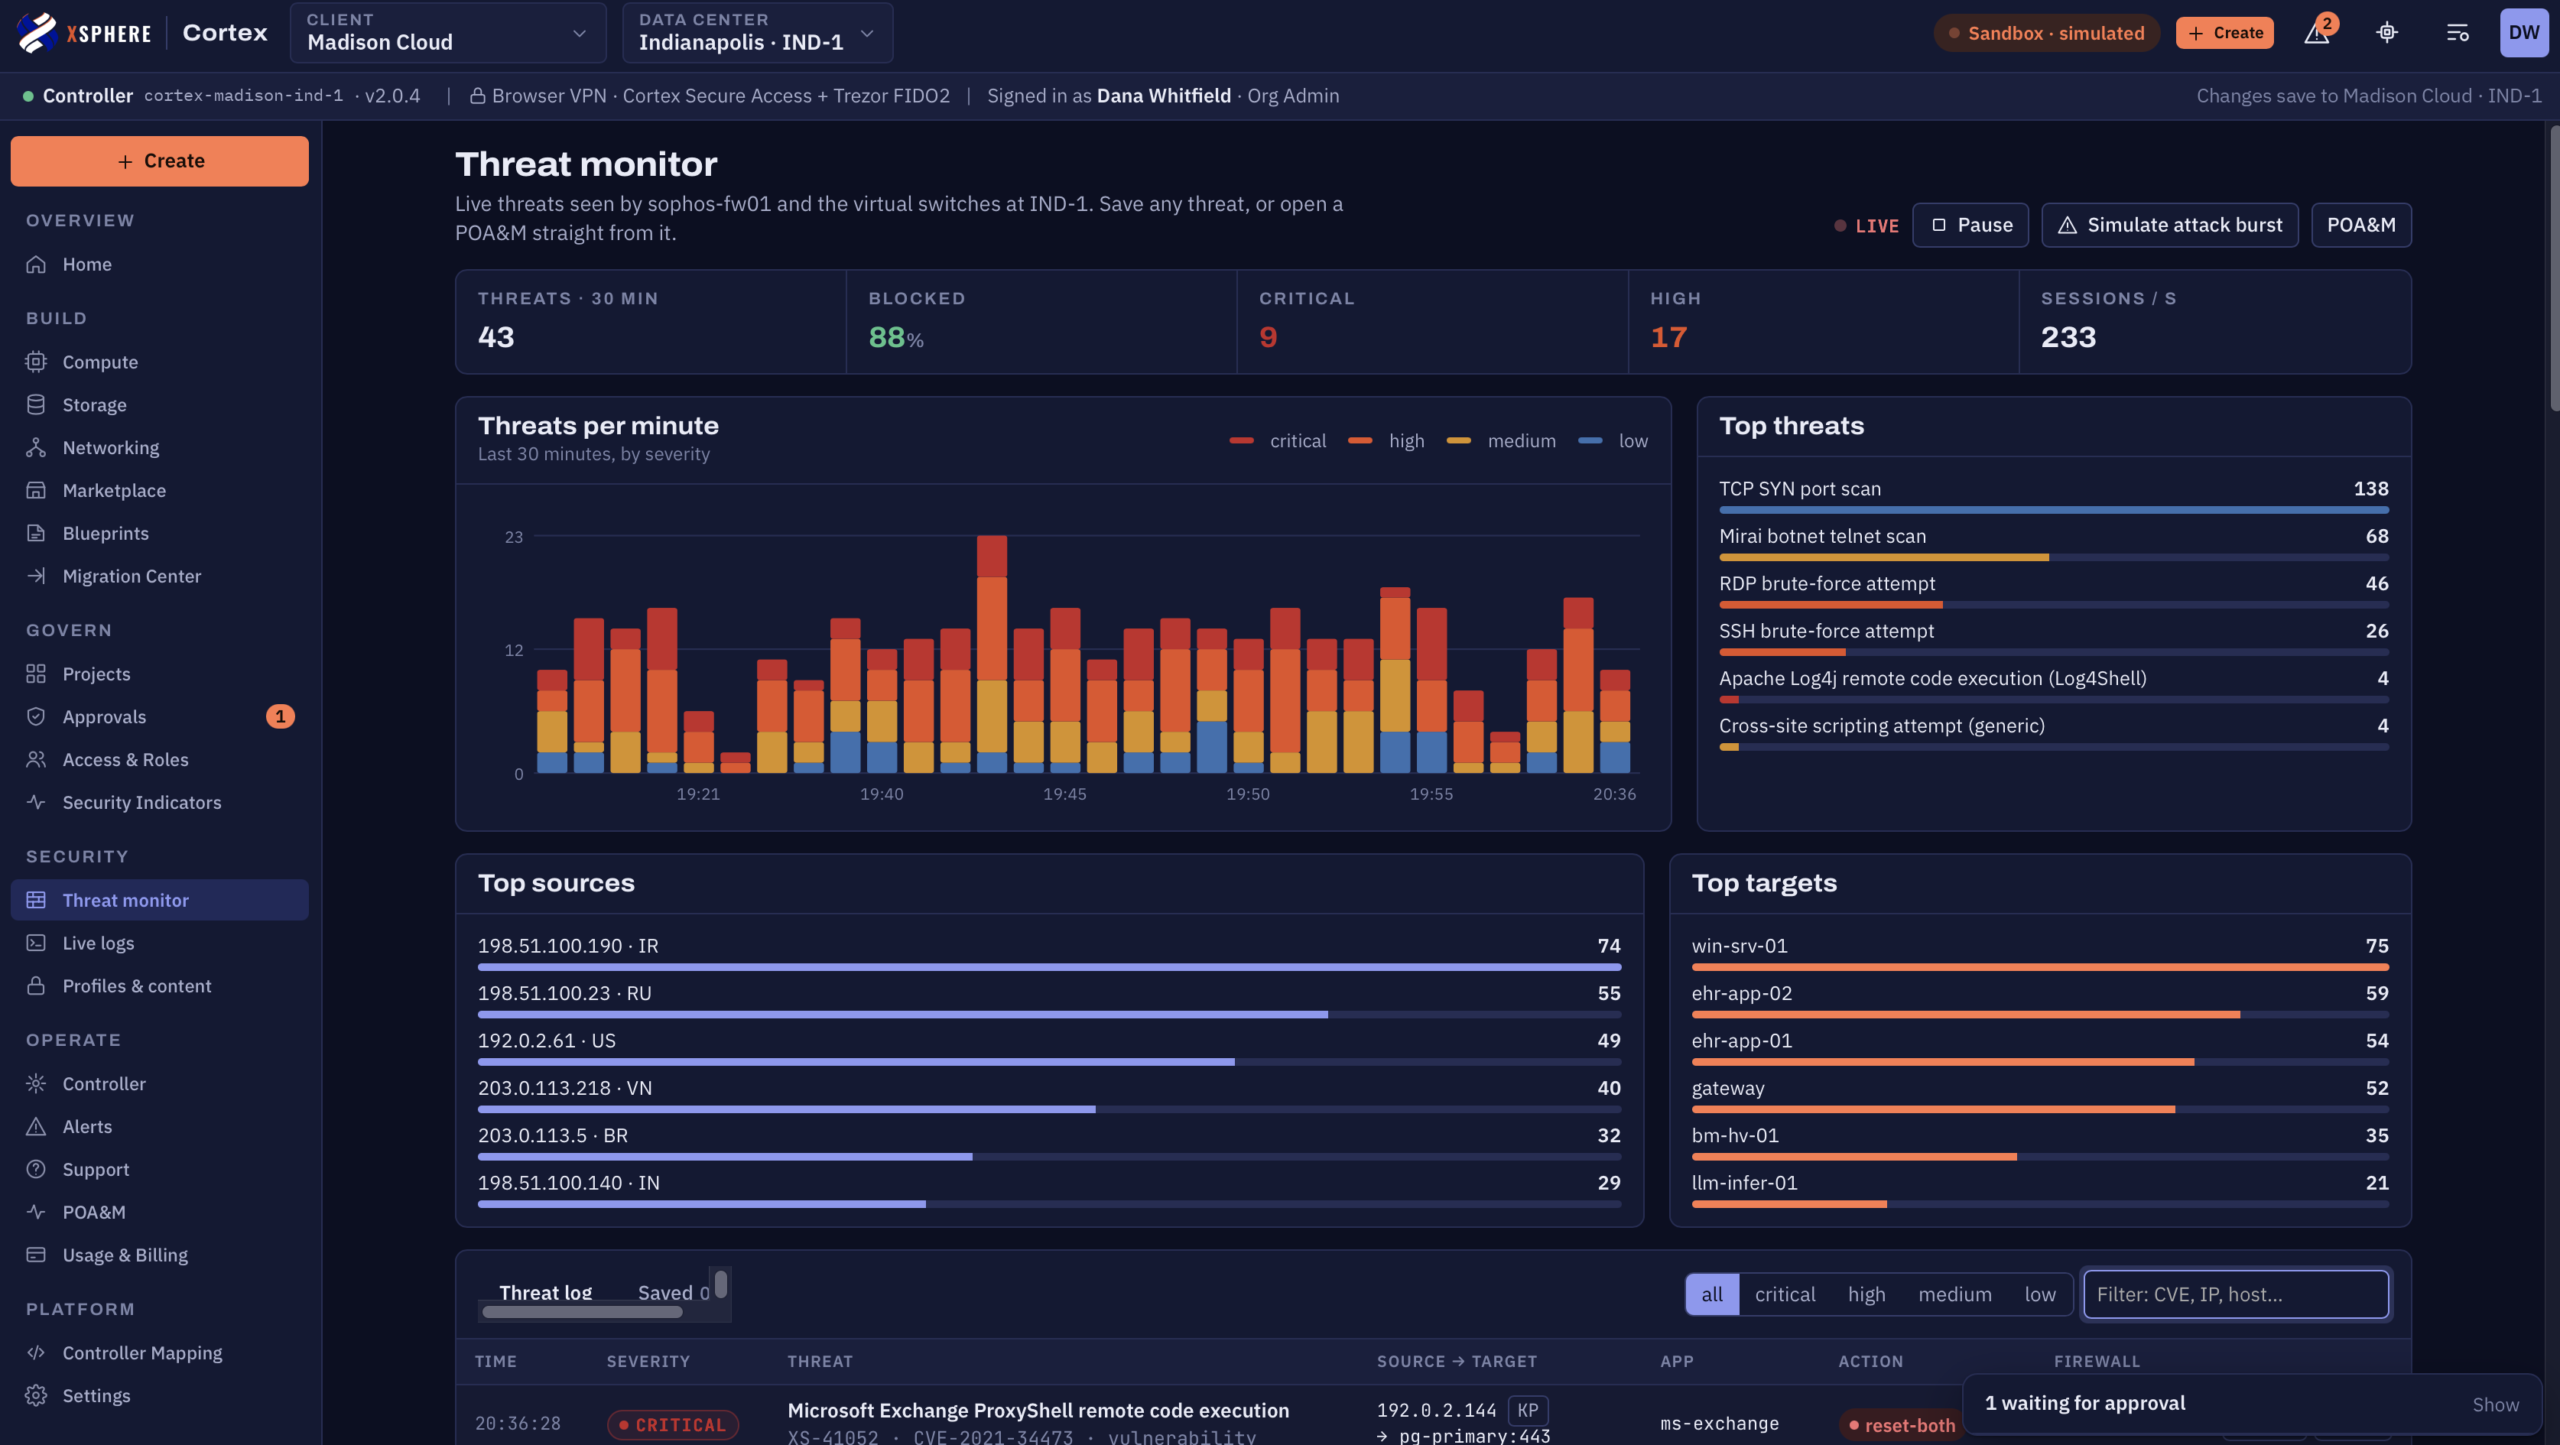
Every Xsphere private cloud includes live threat monitoring across its firewalls and virtual switches. Cortex shows threats as they happen, ranked by severity, with the top attack types, sources, and targeted workloads in a single view. Your team can drill into any event, save it for investigation, or open a POA&M (Plan of Action and Milestones) entry straight from the threat log, turning detection into documented remediation.
Physical & Architectural Isolation
Continuous Compliance
via Key Security Indicators (KSIs)
via Key Security Indicators (KSIs)
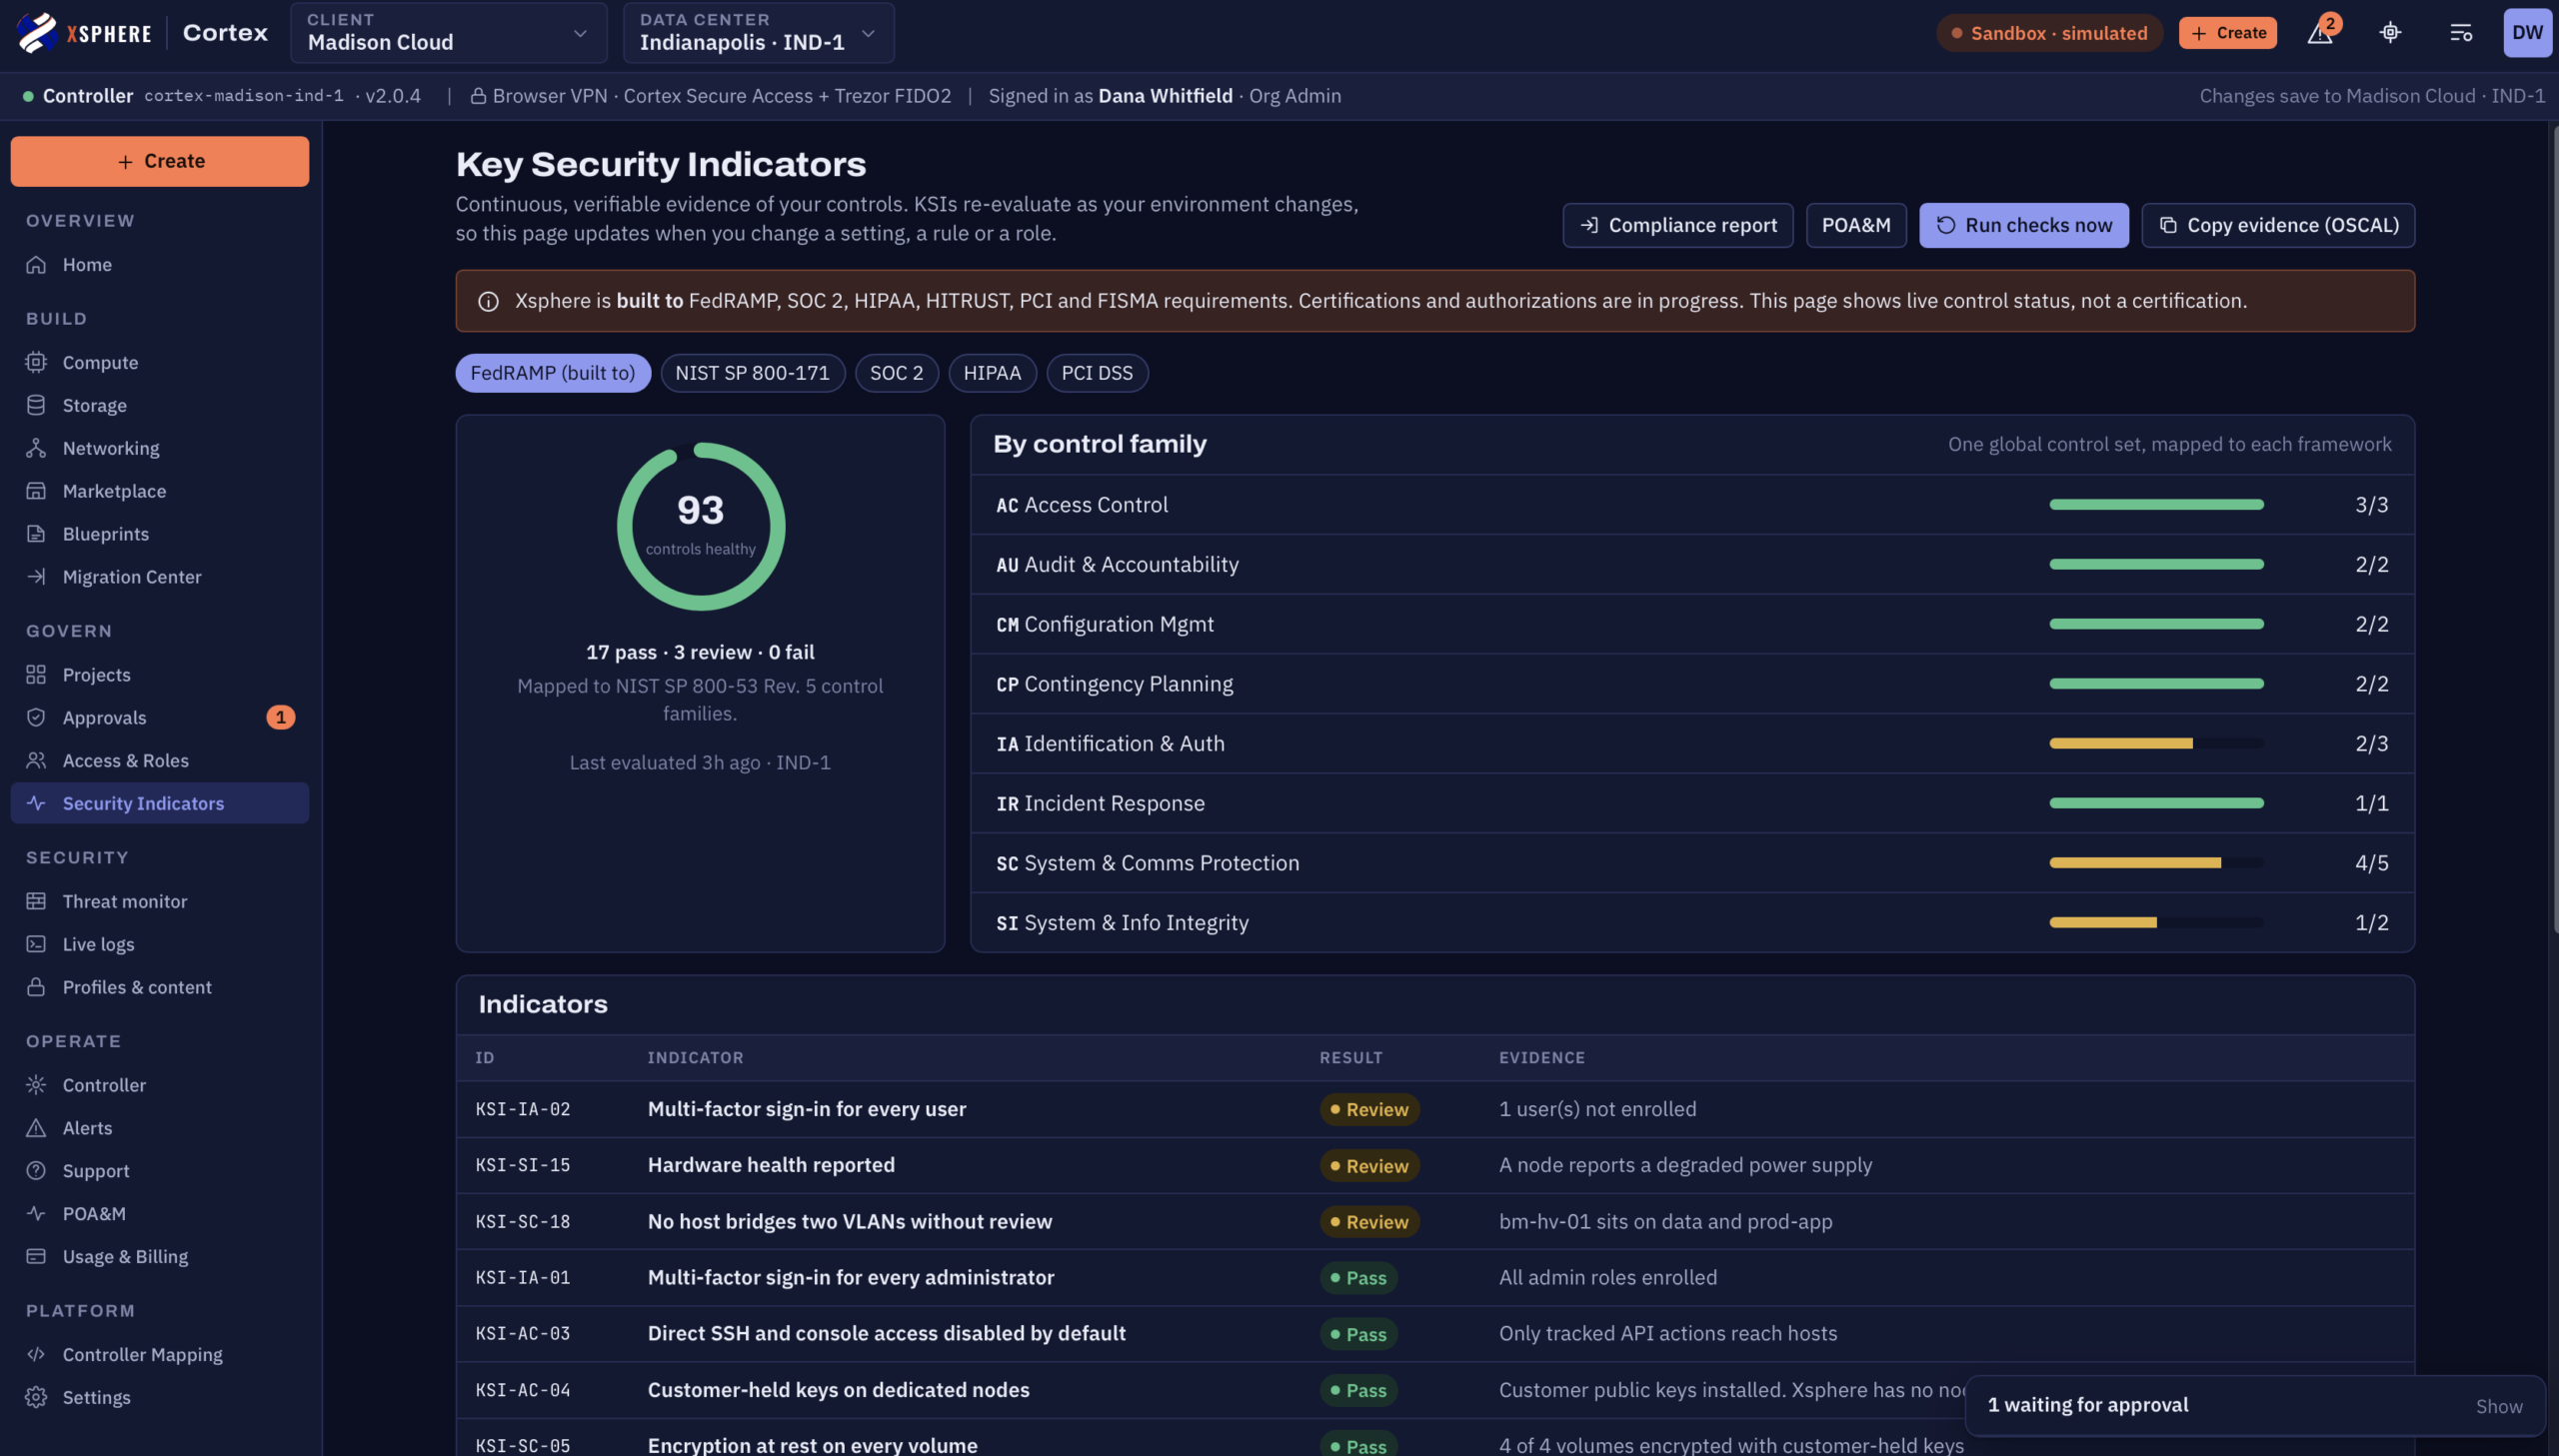
Traditional compliance relies on point-in-time snapshots. Xsphere exposes live Key Security Indicators (KSIs) directly in the Cortex GUI and via API, so you can integrate continuous control verification directly into your applications and automated audit pipelines.
Frameworks engineered to highest security standards
CMMC
CMMC-Ready Infrastructure
Xsphere Cloud helps defense contractors and their supply chains meet Cybersecurity Maturity Model Certification (CMMC) requirements. Our private cloud runs on a hardened, FedRAMP-aligned security stack that maps to the NIST SP 800-171 controls behind CMMC Level 2. That gives your Controlled Unclassified Information a secure, U.S.-based home with continuous monitoring, strong access controls, and audit-ready documentation.
Xsphere’s security stack is built to FedRAMP-aligned standards, and Xsphere is actively pursuing FedRAMP authorization.